WireGuard vs OpenVPN Speed in 2026: Which Protocol Is Faster?
WireGuard vs OpenVPN speed compared across downloads, latency, reconnects, routers, and restricted networks—with a repeatable test method and a clear protocol recommendation.
Networking Editorial
Quick Answer
WireGuard is usually faster than OpenVPN on the same device and server. It has less protocol overhead, establishes tunnels faster, and normally uses less processor time an advantage that becomes especially visible on phones and consumer routers. Choose WireGuard for everyday browsing, streaming, gaming, and downloads. Keep OpenVPN available for restrictive networks, legacy hardware, or cases where OpenVPN TCP connects more reliably than UDP based WireGuard.
| Test area | WireGuard | OpenVPN | Winner |
|---|---|---|---|
| Download throughput | Usually retains more of the base connection | More CPU and protocol overhead | WireGuard |
| Latency | Usually adds less delay | Normally adds more processing delay | WireGuard |
| Connection time | Near instant on modern apps | TLS negotiation takes longer | WireGuard |
| Network switching | Fast recovery between Wi Fi and mobile data | May require a longer reconnect | WireGuard |
| Restricted networks | UDP can be blocked | TCP 443 can resemble ordinary HTTPS traffic | OpenVPN |
| Older hardware | Low processing overhead | Can saturate a weak router CPU | WireGuard |
How to Run a Fair WireGuard vs OpenVPN Speed Test
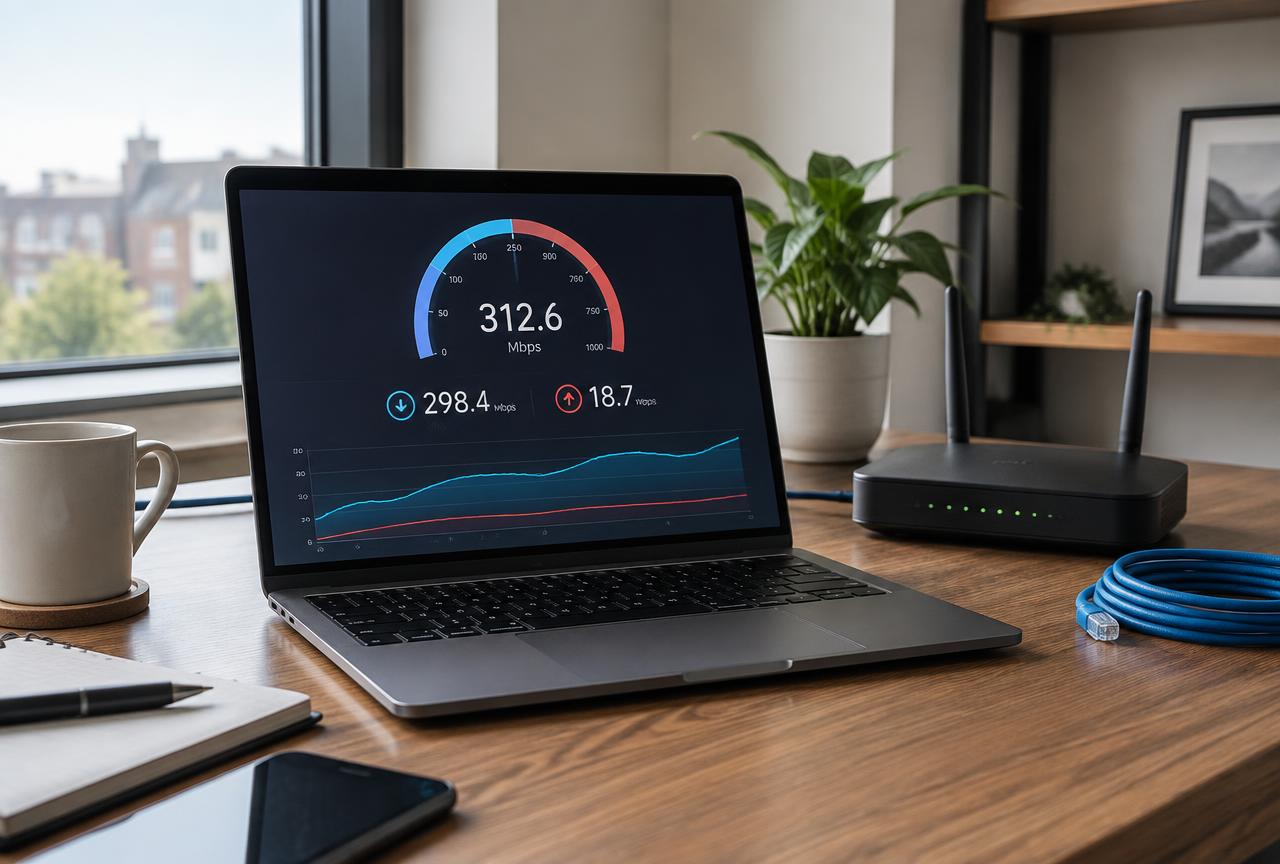
A single speed test screenshot proves very little. Internet routing, server load, Wi Fi interference, and the test endpoint can change from one minute to the next. A fair comparison controls those variables and repeats each measurement. The process below gives you a result that reflects your own device and network rather than a provider's best case marketing figure.
Measure the connection without a VPN
Run three tests with the VPN disconnected. Record the median download speed, upload speed, and idle latency. This baseline shows how much performance each protocol retains.
Choose one nearby VPN server
Use the same city and, where the app allows it, the exact same server for both protocols. A nearby server reduces the effect of physical distance and international routing.
Test WireGuard three times
Select WireGuard or the provider's WireGuard based option, connect, wait thirty seconds, and run three tests. Record the median rather than the highest result.
Test OpenVPN UDP three times
Change only the protocol. Keep the device, server location, Wi Fi or Ethernet connection, and speed test endpoint unchanged. OpenVPN UDP is the fair performance comparison; TCP is designed for compatibility rather than maximum speed.
Repeat at a second time of day
Run the sequence once more during a busy evening period. If both protocols slow down equally, server or ISP congestion is more likely than protocol overhead.
Compare retained speed and stability
Divide each VPN result by the no VPN baseline to calculate retained speed. Also note disconnects and large swings between runs; a slightly slower stable tunnel is more useful than one isolated peak.
Why WireGuard Is Usually Faster
WireGuard was designed as a small, modern VPN protocol with a fixed set of cryptographic choices. Its lean packet format and efficient implementation reduce the work required to encrypt, route, and decrypt each packet. OpenVPN is more configurable and mature, but that flexibility brings a larger software stack and more processing overhead.
The difference is often modest on a powerful desktop with a slower broadband line because neither protocol reaches the machine's limits. It becomes larger on gigabit connections, battery powered devices, and low cost routers, where OpenVPN can consume all available processor capacity before the internet connection itself is saturated.
Latency, Gaming, and Video Calls
WireGuard normally adds less processing delay, but server distance remains the larger factor. Connecting to a nearby WireGuard server can preserve responsive gaming and calls; connecting to a server across an ocean will still add substantial latency. A VPN cannot beat the physical route to the destination, and it should not be sold as a guaranteed ping reducer.
The Difference Is Bigger on Routers
Consumer routers have much weaker processors than laptops and phones. OpenVPN encryption can become the bottleneck long before a fast fiber or cable connection is fully used. WireGuard's lower overhead lets compatible routers move more encrypted traffic with the same hardware, which is why protocol choice matters most when one tunnel protects an entire home network.
Do not assume that every router supports WireGuard, however. Many stock firmware interfaces accept only OpenVPN configuration files. If the router offers both clients, test both. If it offers OpenVPN only, a newer VPN capable router may deliver a larger improvement than changing providers.
When OpenVPN Is Still the Better Choice
- A school, hotel, office, or public network blocks UDP traffic used by WireGuard.
- OpenVPN TCP on port 443 connects where other VPN protocols fail.
- A legacy router or operating system does not support WireGuard.
- An organization requires certificate based authentication or specific cipher controls.
- The particular OpenVPN server is less congested than the available WireGuard server.
Does the VPN Provider Matter More Than the Protocol?
Sometimes. Protocol efficiency cannot compensate for an overloaded server, poor international routing, or limited network capacity. A well run OpenVPN server can outperform a congested WireGuard server. That is why a VPN purchase should be based on server quality, independent audits, app reliability, and refund terms as well as the protocol list.
NordVPN uses NordLynx, its WireGuard based protocol, and is our overall pick when speed is the main buying criterion. Surfshark also offers WireGuard and is the lower cost option for households that need unlimited simultaneous devices. The correct choice is the one that performs consistently on the routes and devices you actually use, so make use of the refund period and run the controlled test above.
| Priority | What to check | Why it matters |
|---|---|---|
| Protocol | WireGuard or a transparent WireGuard based option | Lower overhead and faster reconnects |
| Server choice | Multiple nearby cities and visible load where available | Distance and congestion affect speed |
| Router support | Manual configuration files and current setup guides | Protects devices without native VPN apps |
| Kill switch | System level traffic blocking | Prevents exposure during reconnects |
| Refund policy | Clear money back terms | Lets you test on your own connection |
Common Speed Test Mistakes
- Testing different server cities and attributing the routing difference to the protocol.
- Comparing one unusually high result instead of the median of repeated runs.
- Running one test over Ethernet and the other over variable Wi Fi.
- Comparing WireGuard with OpenVPN TCP rather than OpenVPN UDP.
- Testing at different times while server and neighborhood network load changes.
- Ignoring reconnect time, packet loss, and stability because the headline download number looks good.
Verdict: Use WireGuard by Default
For most people, WireGuard is the right default in 2026. It is normally faster, reconnects quickly, and places less strain on phones and routers. OpenVPN remains valuable rather than obsolete: switch to OpenVPN UDP if a specific WireGuard route performs poorly, or OpenVPN TCP when a restrictive network blocks the faster option. Test both against the same baseline, then keep the protocol that delivers the best combination of retained speed and stability on your connection.
Is WireGuard faster than OpenVPN?
Usually, yes. WireGuard has less protocol and processing overhead, so it generally retains more download speed and adds less latency on the same device and server. Server congestion and routing can still reverse an individual result.
How much faster is WireGuard than OpenVPN?
There is no honest universal percentage. The difference depends on your processor, operating system, connection speed, server load, and route. It is often most noticeable on gigabit connections and consumer routers where OpenVPN becomes limited by processor performance.
Is WireGuard better than OpenVPN for gaming?
WireGuard is normally the better first choice because it adds less processing delay and recovers quickly after network changes. A nearby, uncongested server matters more than the protocol alone, and no VPN can guarantee lower ping.
Should I use WireGuard or OpenVPN on a router?
Use WireGuard when the router supports both. Its lower processor overhead usually provides better throughput on modest hardware. Use OpenVPN when it is the only supported client or when you need its broader compatibility.
Is OpenVPN safer than WireGuard?
Both are considered secure when implemented and configured correctly. WireGuard uses a smaller codebase and fixed modern cryptography; OpenVPN offers mature, configurable TLS based security. Speed, compatibility, and network conditions are usually the deciding factors for consumers.
Why is OpenVPN faster in my test?
The OpenVPN server may be less congested or use a better route, or your provider may operate separate infrastructure for each protocol. Repeat the test on the same server location and at another time before drawing a conclusion.